


2026-11-11 04:26:15
This is simultaneously the most boring yet exciting blog title I've written in a long time. How you pay for services isn't exactly a sexy topic, but it solves a problem that's been a massive bugbear for a long time.
Here's a brief history of the issue: many organisations have policies that make it extremely hard to purchase goods and services with a credit card. I wrote about this more than two years ago now, where I referred to "Neville" in the procurement department who, because "reasons", demanded an invoice in advance and payment via electronic funds transfer (EFT) only. That ultimately means the world's most popular way to make online payments is out of reach for them. Unfortunately, until today, that was the only way we could take payment via Stripe, which processes all our online HIBP purchases. That left only two options for orgs in this situation:
The problem with the first option is obvious. The second option "solved" the first problem by allowing a company to pay a reseller by EFT, who then paid us by card. The reseller would then mark the price up (often significantly), slow the whole process down, log countless tickets with us (despite the existence of a dedicated portal for them), and frankly, just be a pain in the arse for everyone. It's hard to express the level of disdain I have for most resellers, and I even still have a 1,381-word draft blog post titled "That's it - Resellers are now Banned from Have I Been Pwned", which I held back from posting. Why? Because I've walked in the shoes of the folks trying to purchase our services who are just trying to get their job done, and Neville has told them they can't pay by card. That was me in a previous life, and it sucked. We kept resellers solely to support those people.
But today, HIBP's subscription page has something all new on it:
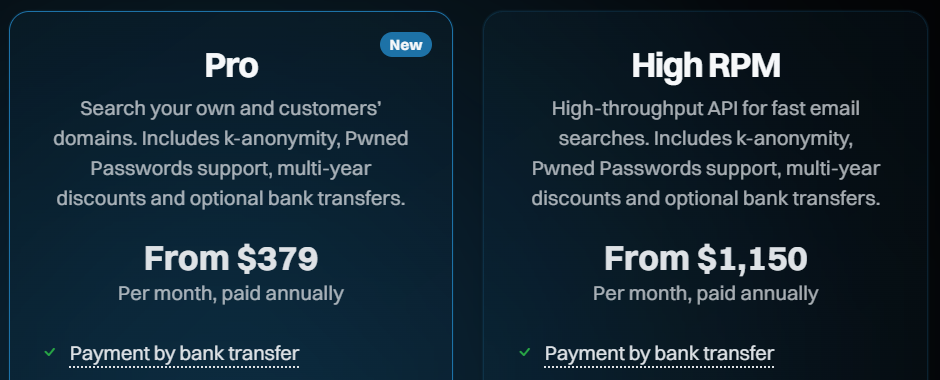
Stripe has given us early access to EFT payments in Australia. They've been available in the US for a while, but as an Aussie company and with global financial systems being what they are (i.e. not always the most flexible), we just didn't have that option. Until now. So, we've added EFT as a payment method to our Pro and High RPM plans and kept the entry-level Core ones on card only, as there's some additional overhead on our end. You'll see these every time you go to purchase an eligible subscription:
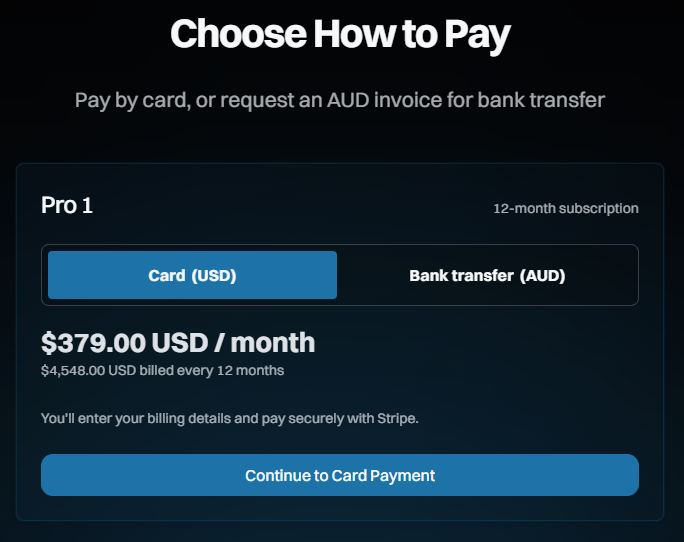
When you choose to pay by bank transfer, you're given a form for your company details (this is how we calculate any applicable taxes), then a Stripe payment link which loads something similar to the following:
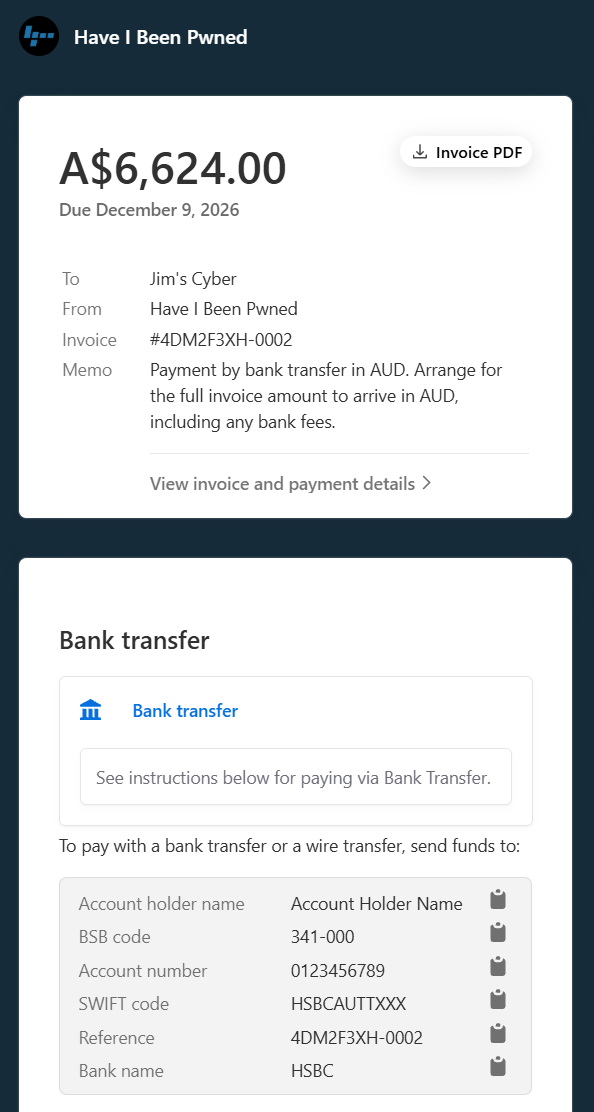
The first thing is that, being an Aussie company with an Aussie bank account, we need to reflect EFT payments in AUD rather than USD. It makes sense when you think about it: we do USD for all the existing products paid for by card, and whatever the FX conversion gods decide is the corresponding Aussie amount eventually lands on our end. But that's a model where the card is charged, and access is granted immediately. For EFT, funds flow through the wires, do FX conversion for non-Aussie purchasers, land in the target account and then Stripe webhook magic enables the service. We need that exact amount to land on our end, so we can't be rolling the dice on what exchange rate we're going to get; hence, Stripe requires us to charge in the target currency. The products are exactly the same price based on the rate we currently see via Stripe purchases today (about 69 American cents per Aussie dollar), we'll just have to see if that's revised in the future with any major currency fluctuations.
Next are the banking details. Pretty straightforward, and I'm sure we've all made payments to an account like this before. The main thing is that the account number is a virtual one, which is how Stripe reconciles money that comes in from a previously raised invoice. When you sell a very limited number of products and a bunch of customers are buying the same one, this is how Stripe is then able to reconcile who has paid for what. If you really want to geek out on bank payments, Stripe has a dedicated EFT explainer page.
And finally, subscriptions in HIBP begin as soon as the invoice is raised, but access to the service only begins when payment is made. You can see the problem if we didn't do it this way: bad guy spins up the service and immediately starts using it then just never pays. But this all ties into the quote ecosystem in the existing HIBP dashboard, so it's easy to generate a quote, go flick it to Neville, get it approved, then raise and pay the invoice straight away.
As I said in the opening, it's not the most exciting topic, but it's a major thing for us and the customers who were left with only bad options if they genuinely couldn't pay by card. In the aforementioned draft blog post on binning resellers, I'd written about how we'd seen markups of up to 131% (so yes, more than double the price!), with absolutely zero value add (i.e. they don't do any product support, that remains entirely on us). But the burden resellers really put on us is the support they require to make purchases; in that same draft post, I calculated that resellers accounted for 0.86% of all sales but 43% of all support tickets. That's just nuts, especially for such a small team (although Bruce has helped enormously).
We hope this makes life easier for a bunch of people who were previously stuck between a rock and a hard place, and that includes all the "Nevilles" out there too. This is all now live and accessible via the pricing page. If you run into any issues, Bruce is standing by in the support portal.
2026-11-10 08:42:35
The kids-and-social-media discussion is just dumb. It's not the premise of delaying their access until 16, but the inability of those who should know better to grasp where the responsibility for enforcement lies. Here's our PM's explainer after the laws passed down here a couple of years ago:
The onus won't be on parents or young people. There will be no penalties for users.
And it's been expressed many times since, in similar terms, always to the effect of placing responsibility for implementation and enforcement on the social media platforms. Inevitably, there are some massive holes in their implementation, along with major privacy and social concerns. But as I say this week (and have said on many previous occasions), it doesn't have to be perfect; over the long run, it will gradually change social norms, and the kids in that shoulder age bracket right now will have a different set of expectations than those who come after them. But hopefully, in the interim, the whole "onus won't be on parents" mantra will be respected more than it has been to date.


2026-11-01 15:35:23
By pure timing coincidence, the Proton CEO's AI @ Proton, Engineering Manifesto made headlines around the same time as this week's video. The guy's management style and choice of language have really rubbed a lot of people up the wrong way, and deservedly so, IMHO. However... this section of his screed really resonated with me:
Your job has fundamentally changed. It is no longer to write code, and LLMs are not here to help you write better code faster. Your job is to help the LLM write better code faster.
Dev jobs as we know them are gone. Dead. And if you disagree, you're in for a shock in the very near future. But at the same time:
I don't remember the last time tech has been this exciting. It's white hot right now. Anyone who loves technology and computers is probably having a great time right now.
— Jack Rhysider 🏴☠️ (@JackRhysider) October 30, 2026
Yes! This! Not handwriting code "old school" isn't something to lament; rather, our unprecedented ability to innovate, create and build things that are meaningful to us is something to be enormously excited about. Anyway, on that topic:
2026-10-27 15:59:09
As the news from last week has settled down, it would seem this headline was pretty spot on. The foretold apocalypse didn't eventuate, and there were no internet-destroying outages. In fact, it took days before I could find a single story of PHP2Shell being reliably attributed back to a breach. And I don't think we can say the relatively benign outcome was only achieved because we did take it so seriously either; there's a massive trove of sites out there that have been left to rot and would have every opportunity to be pwned by a bug of this magnitude that was readily exploitable, yet here we are. Which is good 🙂
2026-10-19 14:47:58
I have this sense that we've passed the point where "vibe coding" is a derogatory term. I have no empirical evidence for this; it's more a feeling that those weaponising the term have now accepted the inevitability and are just getting with the program. Or they've reskilled into other industries because, let's face it: you can't be a productive, competitive developer today without AI. I saw this comment from Linus Torvalds today which I thought really nailed it:
‼️ Linus Torvalds called rules against AI coding tools "UTTERLY STUPID" on the Linux kernel mailing list. He says people he respects and calls intelligent do not shy away from using new tools. https://t.co/HaQ8H4BrVc
— International Cyber Digest (@IntCyberDigest) October 17, 2026
He's always had a way with words 🙂 Anyway, here's what we're doing:
2026-10-13 18:47:27
I remember the name of that AI doco now - The AI Doc: Or How I Became an Apocaloptimist. I was watching it on the long-haul flight home the other day, and what I found particularly engrossing was the polar-opposite opinions from a bunch of people: "it's gonna kill us all" versus "it's gonna make us all rich", and so on. But to some extent, I can understand the gap between opinions when we're all just speculating about the future. I have much less understanding for why people infatuate with hyping AI as a data breach monster when the evidence to date is quite the opposite. In fact, I've enjoyed sharing example after example of recent breaches perpetrated by kids with a telephone (vishing), while pointing out I haven't seen a single one orchestrated by AI.
Speaking of AI, a big thanks to this week's sponsor who's doing gtreat things in the agent observability space, Origin. The machines may not be dumping data that lands in HIBP (yet), but they do go off-script and Origin will help trace back precisely what happened when it all goes wrong.


